NEW QUESTION 41
You are managing a Kubernetes cluster for a company with multiple teams working on different projects. You want to implement RBAC to ensure each team has access only to the resources they need.
See the solution below with Step by Step Explanation.
Explanation:
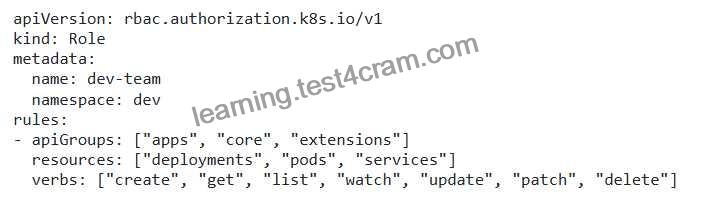
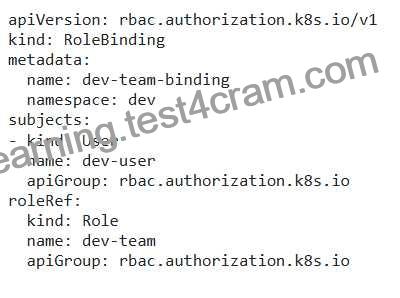
Team A (developers) needs to create and manage deployments, pods, and services in the “dev” namespace.
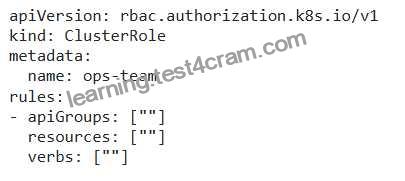
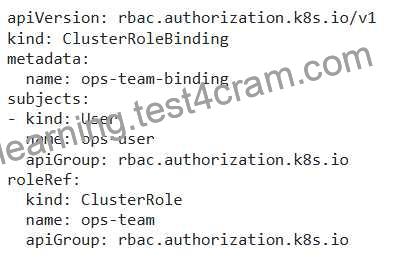
Team B (ops) needs to manage the cluster’s overall health and can access all resources in all namespaces.
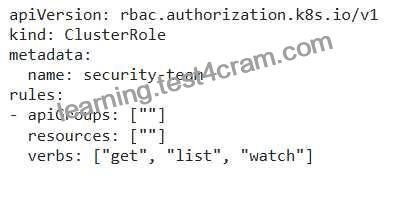
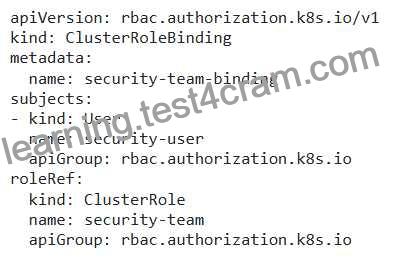
Team C (security) needs to audit and monitor all cluster activity but cannot modify any resources.
Create a YAML file to define the roles and role bindings to implement this RBAC setup.
Solution (Step by Step) :
1 . Create the “dev” namespace:
kubectl create namespace dev
2. Define the “dev-team” role:
3. Create the “dev-team” role binding:
4. Define the “ops-team” role:
5. Create the “ops-team” role binding:
6. Define the “security-team” role:
7. Create the “security-team” role binding:
8. Apply the YAML file to the cluster: kubectl apply -f rbac-config.yaml


