CAS-004 PDF Dumps Sep 16, 2025 Exam Questions – Valid CAS-004 Dumps [Q214-Q230]

Rate this post

CAS-004 PDF Dumps Sep 16, 2025 Exam Questions – Valid CAS-004 Dumps

Ultimate CAS-004 Guide to Prepare Free Latest CompTIA Practice Tests Dumps

QUESTION 214
A company recently deployed a SIEM and began importing logs from a firewall, a file server, a domain controller a web server, and a laptop. A security analyst receives a series of SIEM alerts and prepares to respond. The following is the alert information:

Which of the following should the security analyst do FIRST?


QUESTION 215
A security engineer needs to recommend a solution that will meet the following requirements:
– Identify sensitive data in the provider’s network
– Maintain compliance with company and regulatory guidelines
– Detect and respond to insider threats, privileged user threats, and
compromised accounts
– Enforce datacentric security, such as encryption, tokenization, and
access control
Which of the following solutions should the security engineer recommend to address these requirements?


QUESTION 216
A security engineer is reviewing a record of events after a recent data breach incident that Involved the following:
* A hacker conducted reconnaissance and developed a footprint of the company s Internet-facing web application assets.
* A vulnerability in a third-party horary was exploited by the hacker, resulting in the compromise of a local account.
* The hacker took advantage of the account’s excessive privileges to access a data store and exfiltrate the data without detection.
Which of the following is the BEST solution to help prevent this type of attack from being successful in the future?


QUESTION 217
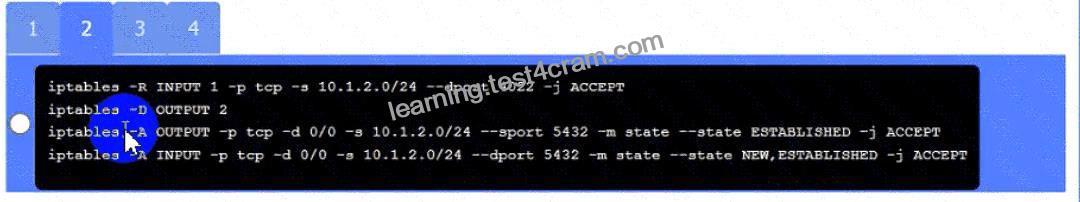
A security engineer needs to review the configurations of several devices on the network to meet the following requirements:
* The PostgreSQL server must only allow connectivity in the 10.1.2.0/24 subnet.
* The SSH daemon on the database server must be configured to listen
to port 4022.
* The SSH daemon must only accept connections from a Single
workstation.
* All host-based firewalls must be disabled on all workstations.
* All devices must have the latest updates from within the past eight
days.
* All HDDs must be configured to secure data at rest.
* Cleartext services are not allowed.
* All devices must be hardened when possible.
Instructions:
Click on the various workstations and network devices to review the posture assessment results. Remediate any possible issues or indicate that no issue is found.
Click on Server A to review output data. Select commands in the appropriate tab to remediate connectivity problems to the pOSTGREsql DATABASE VIA ssh

WAP A

PC A

Laptop A

Switch A

Switch B:

Laptop B

PC B

PC C

Server A


QUESTION 218
In comparison to other types of alternative processing sites that may be invoked as a part of disaster recovery, cold sites are different because they:


QUESTION 219
Signed applications reduce risks by:


QUESTION 220
A security administrator receives reports that several workstations are unable to access resources within one network segment.
A packet capture shows the segment is flooded with ICMPv6 traffic from the source fe80::21ae;4571:42ab:1fdd and for the destination ff02::1.
Which of the following should the security administrator integrate into the network to help prevent this from occurring?


QUESTION 221
A mobile application developer is creating a global, highly scalable, secure chat application. The developer would like to ensure the application is not susceptible to on-path attacks while the user is traveling in potentially hostile regions. Which of the following would BEST achieve that goal?


QUESTION 222
A security auditor needs to review the manner in which an entertainment device operates. The auditor is analyzing the output of a port scanning tool to determine the next steps in the security review. Given the following log output.
The best option for the auditor to use NEXT is:


QUESTION 223
A company has decided to purchase a license for software that is used to operate a mission-critical process.
The third-party developer is new to the industry but is delivering what the company needs at this time.
Which of the following BEST describes the reason why utilizing a source code escrow will reduce the operational risk to the company if the third party stops supporting the application?


QUESTION 224
A security analyst is reviewing the following output:

Which of the following would BEST mitigate this type of attack?


QUESTION 225
A security analyst discovered that the company’s WAF was not properly configured. The main web server was breached, and the following payload was found in one of the malicious requests:

Which of the following would BEST mitigate this vulnerability?


QUESTION 226
In support of disaster recovery objectives, a third party agreed to provide 99.999% uptime. Recently, a hardware failure impacted a firewall without service degradation. Which of the following resiliency concepts was most likely in place?


QUESTION 227
A security analyst is performing a vulnerability assessment on behalf of a client. The analyst must define what constitutes a risk to the organization.
Which of the following should be the analyst’s FIRST action?


QUESTION 228
During a system penetration test, a security engineer successfully gained access to a shell on a Linux host as a standard user and wants to elevate the privilege levels.
Which of the following is a valid Linux post-exploitation method to use to accomplish this goal?


QUESTION 229
A software developer has been tasked with creating a unique threat detection mechanism that is based on machine learning. The information system for which the tool is being developed is on a rapid CI/CD pipeline, and the tool developer is considered a supplier to the process. Which of the following presents the most risk to the development life cycle and to the ability to deliver the security tool on time?


QUESTION 230
An organization is considering a BYOD standard to support remote working. The first iteration of the solution will utilize only approved collaboration applications and the ability to move corporate data between those applications. The security team has concerns about the following:
Unstructured data being exfiltrated after an employee leaves the organization Data being exfiltrated as a result of compromised credentials Sensitive information in emails being exfiltrated Which of the following solutions should the security team implement to mitigate the risk of data loss?


Passing Key To Getting CAS-004 Certified Exam Engine PDF: https://www.test4cram.com/CAS-004_real-exam-dumps.html


Related Links: fortunetelleroracle.com myportal.utt.edu.tt myportal.utt.edu.tt www.stes.tyc.edu.tw www.stes.tyc.edu.tw myportal.utt.edu.tt

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below